As AI agents take on more customer interactions, firms face a growing challenge: ensuring every call, message and engagement complies with regulatory requirements. The AI in Risk and Compliance 2026 report – co-authored by RegTech Analyst and Parker & Lawrence Research – delved into why AI agents are forcing a step-change in contact compliance.
As part of the research for the report, Parker & Lawrence Research interviewed market leaders in the space to discuss contact governance and its changing role in the industry.
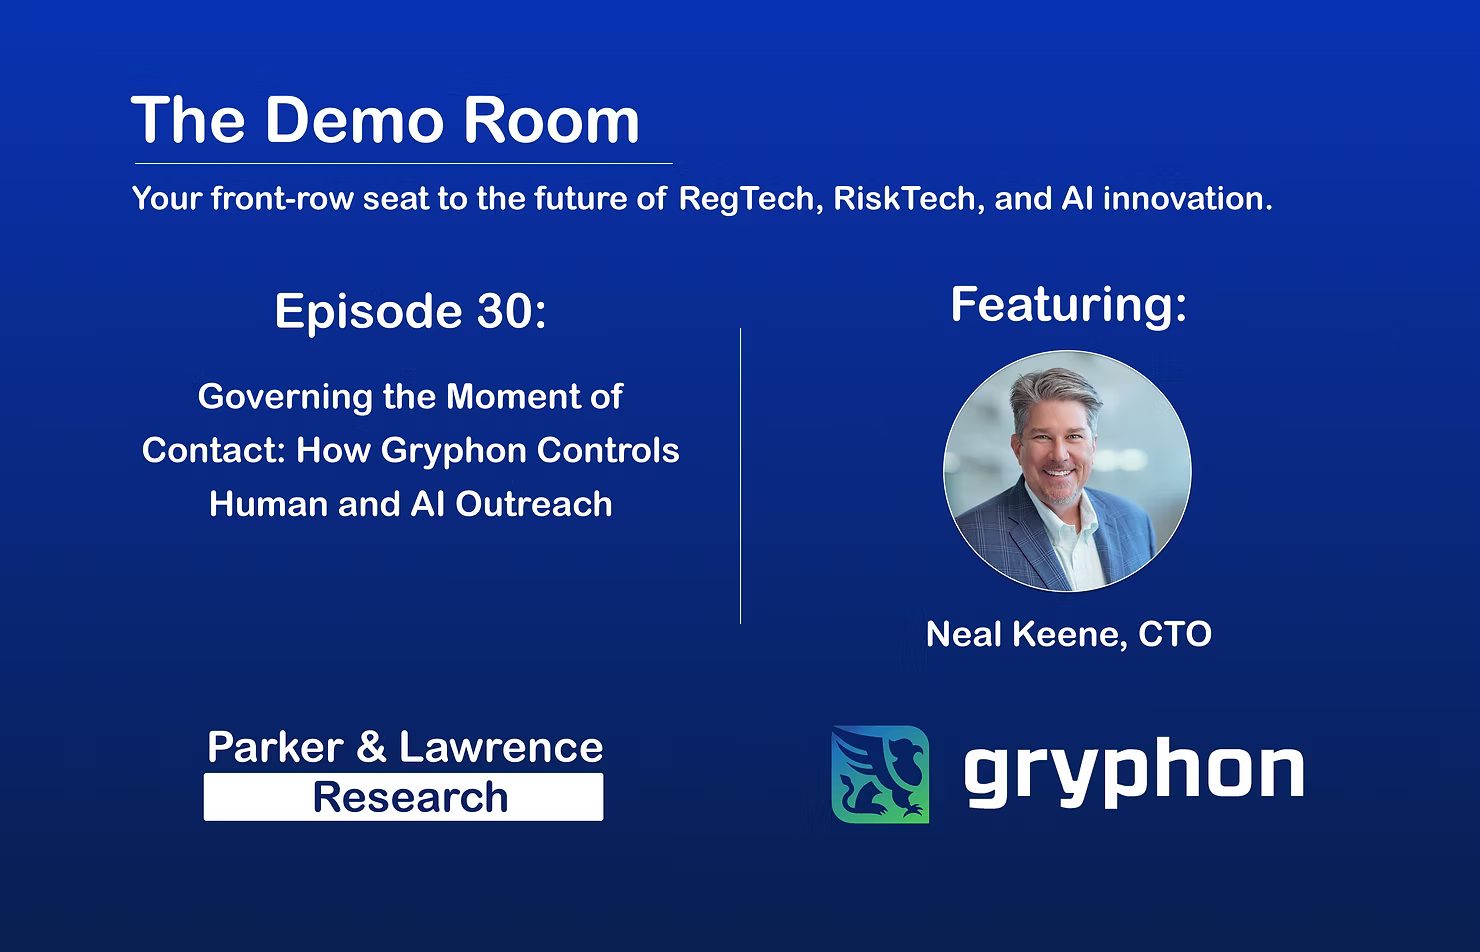
On this occasion, the firm spoke with Neal Keene, CTO at Gryphon, a company that markets Gryphon ONE, which applies regulatory requirements and enterprise policies at the point of customer engagement.
This interview was part of the wider AI in Risk and Compliance 2026 report conducted by RegTech Analyst and Parker Lawrence Research. To download the full report, click here.
As AI agents take on a growing share of customer outreach, the way firms govern contact is coming under strain. Whether a single outbound call is lawful can hinge on consent, do-not-call status, local calling hours, frequency limits and exemptions, all of which shift by channel, purpose and jurisdiction, and can differ from one interaction to the next for the same customer.
The pressure is intensifying. According to 2026 research, 58.4% of reported AI activity now involves AI taking action rather than merely offering information or recommendations. Once AI moves into campaign, CRM and contact-centre workflows, governance has to keep pace at machine speed and across every channel a firm uses.
Many organisations are poorly placed to respond. Contact controls are frequently split across business units and systems, with a call centre, marketing platform and SMS provider each running separate suppression processes. In the US, the stakes are high: the Telephone Consumer Protection Act carries statutory damages of $500 per violation, rising to $1,500 where the breach is wilful or knowing, and claims often arrive as class actions. Yet overly cautious controls carry their own cost, suppressing customers who could lawfully be reached through another channel, at another time or under an exemption.
Traditional post-event sampling offers little comfort. Reviewing 1–3% of interactions after the fact cannot prevent harm when an AI agent handles thousands of conversations, and where liability does not depend on intent, a clean sample does not protect the interactions nobody checked.
Firms also need to reconstruct the inputs, policy, rule version, requester and outcome behind each decision. A generated audit narrative is no replacement for a contemporaneous record.
Gryphon’s answer is a contact governance control layer. Its Gryphon ONE platform evaluates each proposed interaction against regulatory rules, consent and suppression records, contact history, timing, frequency, jurisdiction, channel, purpose and exemptions, returning a permitted, prohibited or conditional result. Conditional outcomes can point to an alternative channel or a required approval.
Crucially, the enforcement path is rules-based rather than probabilistic. Identical inputs produce identical outcomes in milliseconds, at billions of interactions a year and without per-token cost. Language models sit around the control path, helping to retrieve sources, compare new rules against existing policy and draft rule language, but nothing they produce reaches production without expert approval. Client data is protected through tenant isolation, minimisation and redaction, and is not used for model training.
The same controls apply across voice and SMS, whether contact is initiated by a human, an automated campaign or an autonomous agent. Each interaction is tied to its policy, rule version, inputs and requester, with evidence fed into the firm’s GRC environment. Gryphon positions itself one layer below GRC platforms such as Drata and Optro, formerly AuditBoard, and works with Google, Pega, Genesys, Salesforce, Capgemini and Coforge.
Gryphon reports that its controls can recover 35–45% of legally reachable contacts lost to over-suppression, record 100% of governed interactions against a rule version, and cut compliant campaign launch times from months to hours. It governs more than 15 billion interactions a year for one enterprise client.
Read the original post from Parker & Lawrence Research here.
Copyright © 2026 RegTech Analyst
Copyright © 2026 RegTech Analyst